a/eAutoEscapeDEVELOPER GUIDES
HomeGuidesAboutContact
Information
Editorial PolicyPrivacy PolicyTerms of UseCookie PolicyDisclaimer
Menu
HomeGuidesAboutContact

Website information

Editorial PolicyPrivacy PolicyTerms of UseCookie PolicyDisclaimer
Skip to content
  • How to Display User Input Safely (textContent)
    Guides

    How to Display User Input Safely (textContent)

    ByAutoEscape September 10, 2026

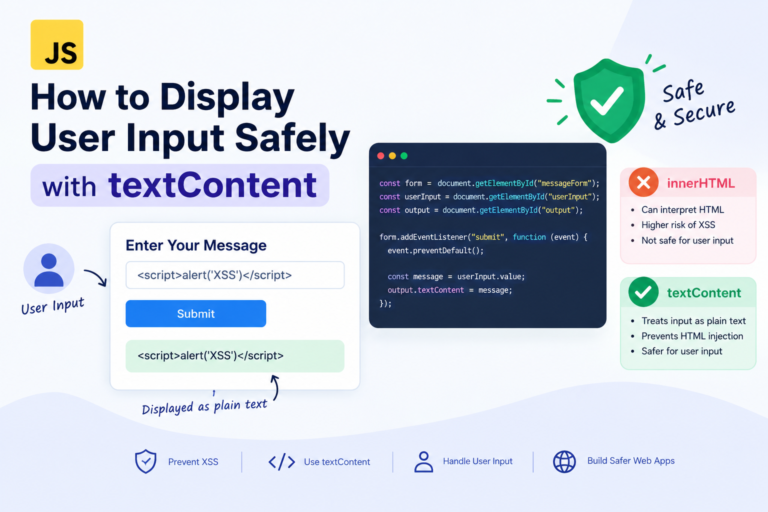
    Anyone that’s ever created a form, comment section, or search box using JavaScript will have had to show something that a user typed on a web page. Well, it seems like a no-brainer, but one thing I’d like to stress is that you should never use user input as HTML, unless you have a good…
    Read More How to Display User Input Safely (textContent)Continue

  • WordPress Output Escaping Guide
    Guides

    WordPress Output Escaping: esc_html(), esc_attr(), and esc_url()

    ByAutoEscape September 8, 2026

    A WordPress website can have dynamic content, like the post title, username, links, and custom fields, or form values. If this information is integrated into a page without proper escaping it can cause security issues, such as cross-site scripting (XSS). There are different functions that WordPress has under its own banner which can help developers…

    Read More WordPress Output Escaping: esc_html(), esc_attr(), and esc_url()Continue

  • Beginner-friendly HTMLHTML5 developer tutorial post titled
    Guides

    Beginner-friendly HTML/HTML5 developer tutorial post titled:

    ByAutoEscape September 4, 2026

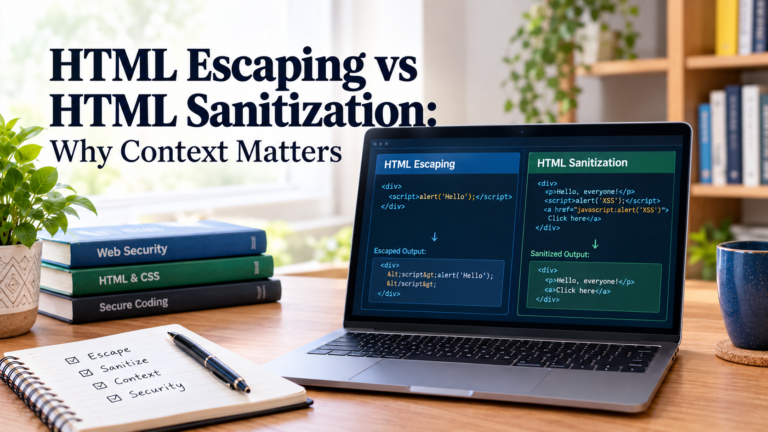
    The difference between HTML escaping and sanitization—in these sometimes-confusing contexts. Introduction HTML escaping and HTML sanitization are two important techniques for protecting websites from cross-site scripting (XSS) attacks. Both offer some protection against the existence of unsafe content that has the potential to pose a security issue, yet both offer different solutions, and in different…

    Read More Beginner-friendly HTML/HTML5 developer tutorial post titled:Continue

  • Malformed JSON in AI-Generated Responses
    Guides

    Malformed JSON in AI-Generated Responses

    ByAutoEscape September 2, 2026

    Malformed JSON in AI-Generated responses can be tackled through a few techniques. AI can create valuable code, data, summaries and auto-responses in seconds. But if you ask for some json from an AI-model, it isn’t always a valid json. Missing quotation marks, after-punctuation commas, extraneous text after the JSON object, invalid character types (unescaped quotes…

    Read More Malformed JSON in AI-Generated ResponsesContinue

Page navigation

Previous PagePrevious 1 2

Small details.
Clean results.

Practical developer guides on JSON, HTML, URLs, regex and Markdown. Clear explanations for the details that matter.

Explore Guides ↗

Explore

  • Home
  • Guides
  • About
  • Editorial Policy

Policies

  • Privacy Policy
  • Terms of Use
  • Cookie Policy
  • Disclaimer

Get in touch

  • Contact
  • support@autoescape.online

Operated by Noah
United Kingdom

© 2026 AutoEscape. Developer guides.

Privacy settings
Scroll to top